Howdy, Stranger!

It looks like you're new here. If you want to get involved, click one of these buttons!


New on LowEndTalk? Please Register and read our Community Rules.

All new Registrations are manually reviewed and approved, so a short delay after registration may occur before your account becomes active.

[Feedback wanted] AdminServer – a lightweight hosting panel for AlmaLinux/Rocky/RHEL (free beta, clo

amerghjjiyeamerghjjiye Member
edited October 12 in General

https://aamrpr.github.io/adminserver-site/
I wanted a hosting control panel that was small, fast, and took isolation and
hardening seriously by default — not as an afterthought. So I built one:
AdminServer, a control panel for RHEL-family servers (AlmaLinux / Rocky /
RHEL 9–10). One server runs several isolated websites, all managed from the
browser — no SSH needed for everyday work.

Here's a look at it:
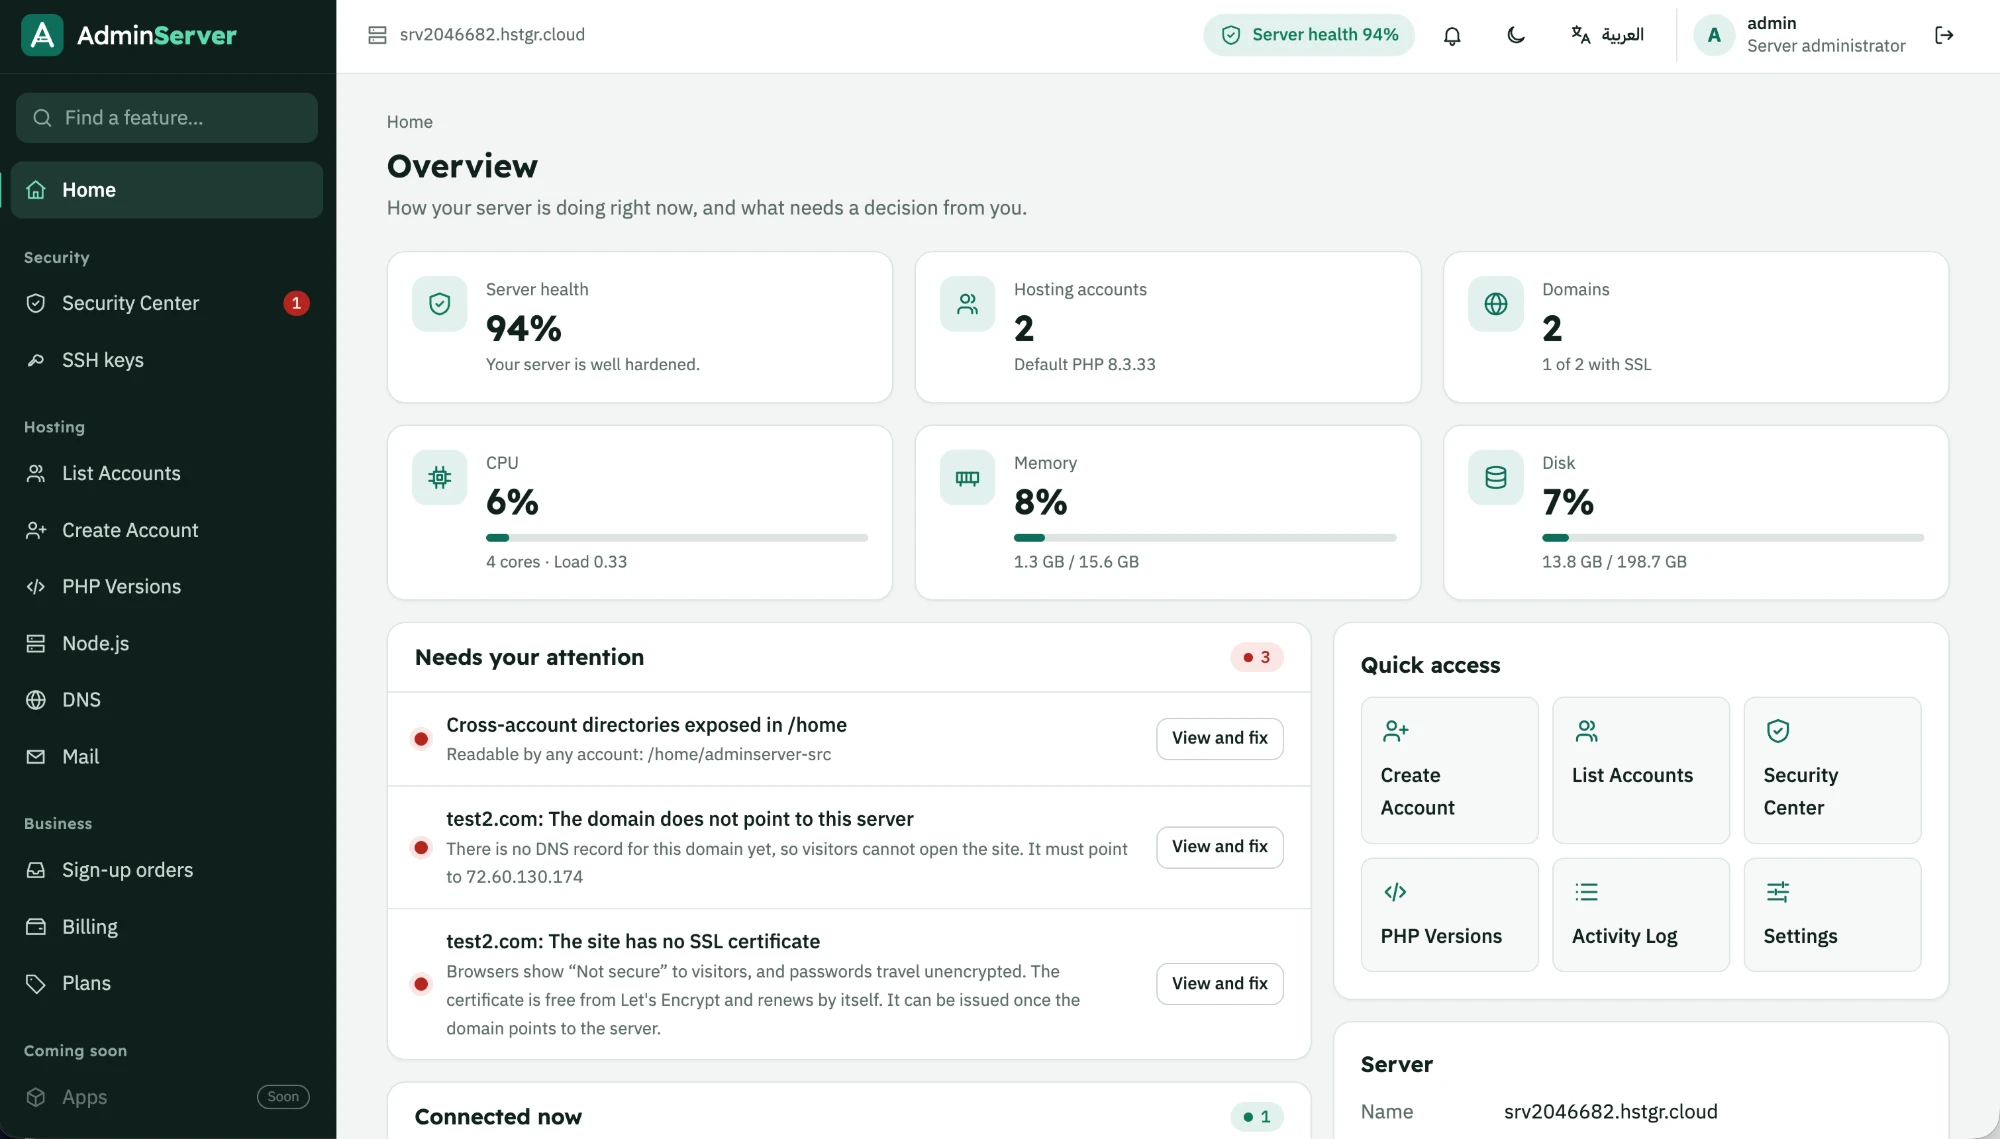
Overview dashboard

What it does

  • Real per-account isolation — each account is its own Linux user and
    systemd slice, with CPU, memory, process and disk limits, enforced by
    SELinux. One site can't read another's files.

  • A Security Center — 28+ hardening checks (firewall, SELinux, SSH, kernel,
    service isolation…), each explained in plain words and fixable in one click,
    with a safe rollback.
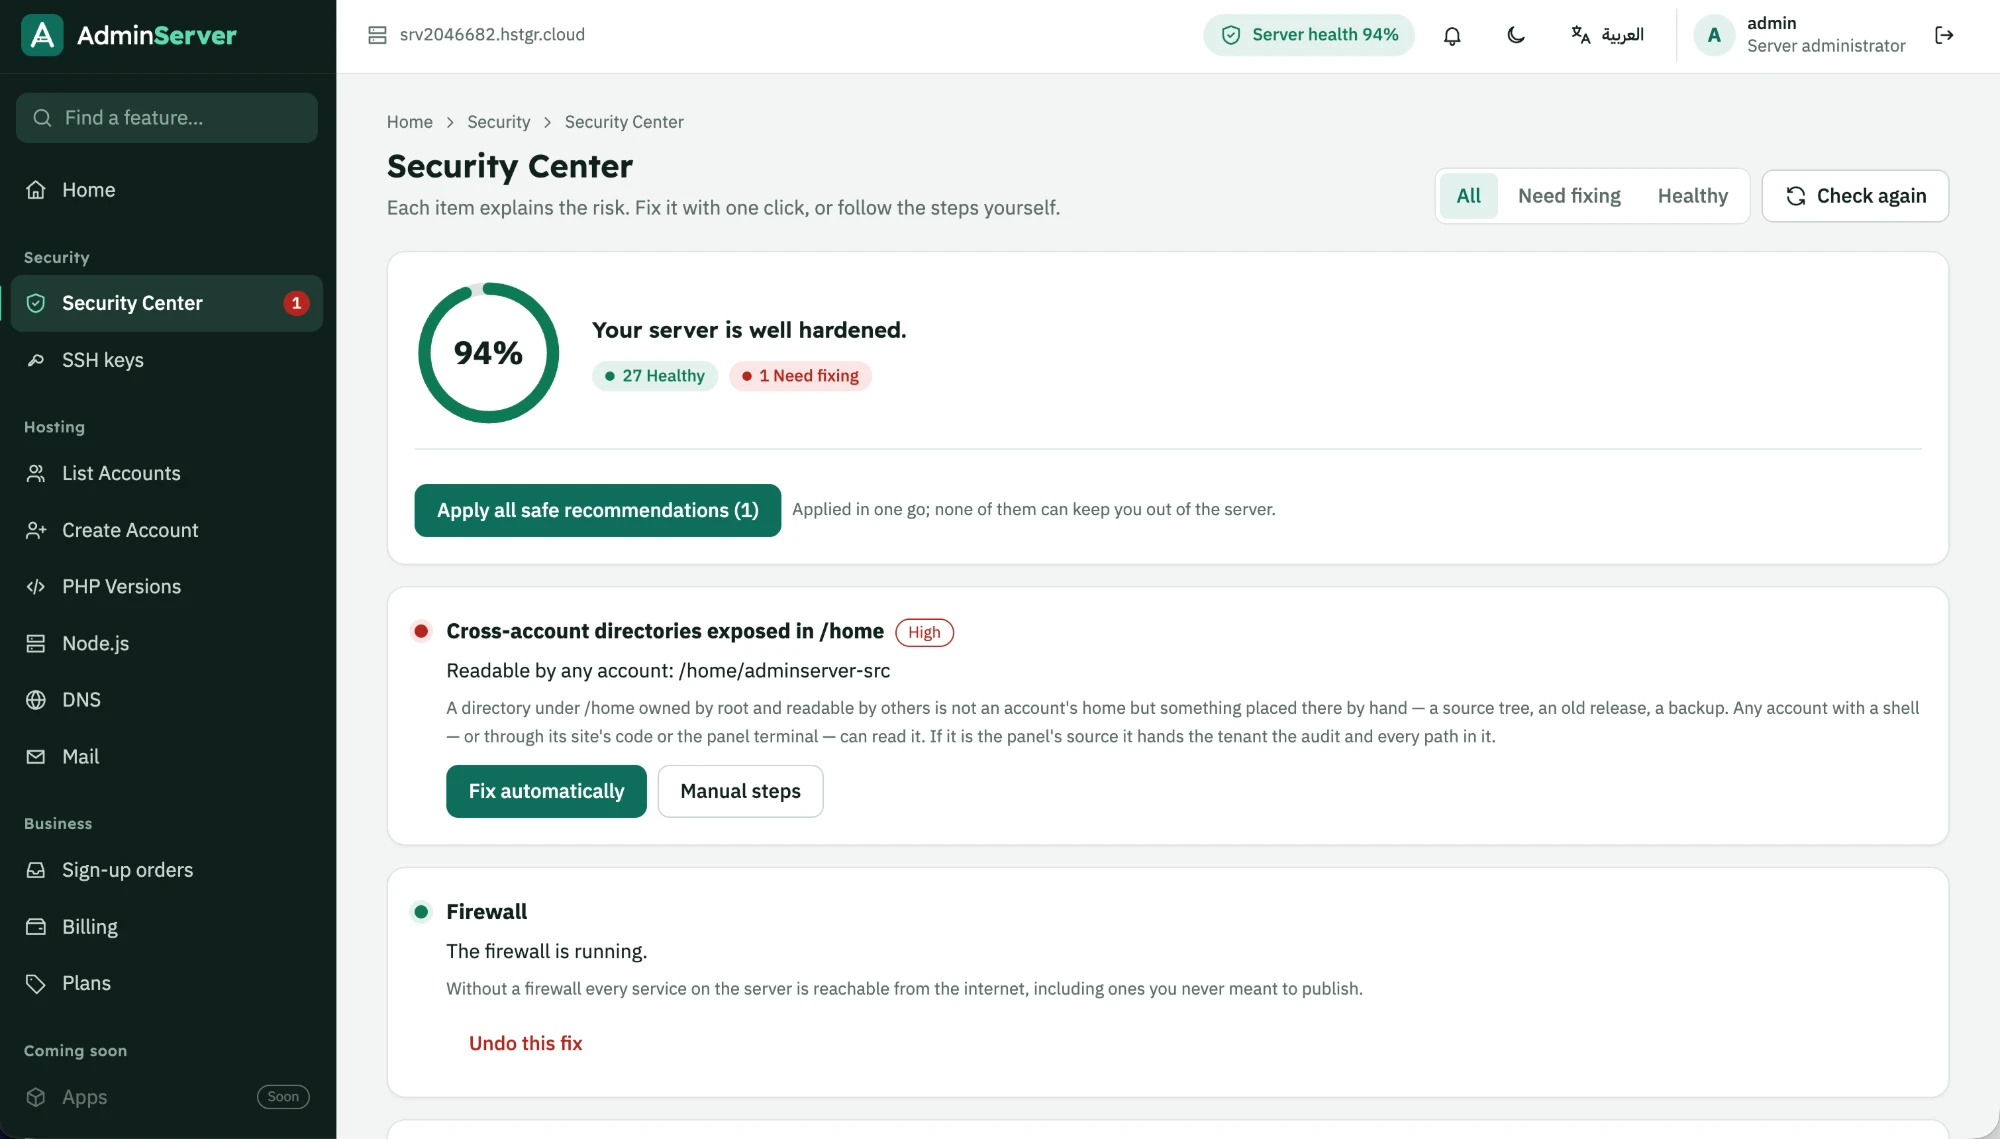
Security Center

  • Per-account and per-subdomain PHP & Node.js — runtimes are installed
    once, centrally, read-only; each site (and each sub-domain, as its own
    mini-site) picks its own version. Node apps run as the account, behind nginx
    over a private socket.

  • Off-server backups — to MEGA or any S3-compatible storage (Backblaze B2,
    Wasabi, Cloudflare R2).

  • The rest — drag-and-drop file manager + Monaco code editor, a web
    terminal that runs as the account, per-site databases + phpMyAdmin, DNS
    (PowerDNS), mail (Postfix/Dovecot), and Let's Encrypt.

  • Signed self-update — updates are verified by checksum and an Ed25519
    signature before install; a tampered package is refused.

  • Bilingual — a full English and Arabic UI.

Try it

On a clean, throwaway AlmaLinux / Rocky / RHEL 9–10 VPS (as root):

```bash
curl -fsSL https://aamrpr.github.io/adminserver-site/install.sh | sudo bash
Comments

  • zedzed Veteran

    subscribe

    Thanked by 1amerghjjiye
  • AlyxAlyx Member, Host Rep

    If only I would get a dollar for each crappy bullshit slop panel out there.

  • One more

    Thanked by 1amerghjjiye
  • @Alyx said:
    If only I would get a dollar for each crappy bullshit slop panel out there.

    You're absolutely right, my friend. That's why I built this control panel and tested it for a full year. It was CLI-only at first, but I've now developed a graphical interface for it. You can try it out and evaluate it, and I genuinely welcome your honest feedback, no matter what it is. Your opinion means a lot to me, my friend.

  • Why this vs the other offerings?

  • @amerghjjiye said: So I built one

    @amerghjjiye said: I've now developed a graphical interface for it

    Even your post is 100% AI generated, says everything.

    Thanked by 1amerghjjiye
  • @SodaWithoutSparkles said:
    Why this vs the other offerings?

    I’ve spent 15 years working in networking and server infrastructure, and throughout that time, I’ve seen many of the same issues across different control panels. Those experiences taught me that building a reliable server management platform requires much more than just creating a user interface. It requires understanding the real-world challenges, edge cases, security concerns, and operational details that developers without extensive infrastructure experience might easily overlook.

    That’s why I started developing this project a year ago, focusing on the details that truly matter in production environments.

    And here’s something important: this project is not for sale, and it will remain 100% free. My goal isn’t to build another commercial alternative, but to create a reliable, practical, and accessible server management platform that everyone can benefit from.

    I believe the best way to improve it is through real-world testing, honest feedback, and collaboration with the community. That’s exactly why I’m inviting people to try it, challenge it, and help me make it better.

  • MurvMurv Member, Megathread Squad

    ADMINBOLT - THE MODERN WEB HOSTING CONTROL PANEL!

  • MurvMurv Member, Megathread Squad

    wait sorry, wrong slop panel thread

  • @luckypenguin said:

    @amerghjjiye said: So I built one

    @amerghjjiye said: I've now developed a graphical interface for it

    Even your post is 100% AI generated, says everything.

    It’s true that ai helped me with the visual identity, but I worked on things far more important than that.

  • AlyxAlyx Member, Host Rep

    @amerghjjiye said:

    @Alyx said:
    If only I would get a dollar for each crappy bullshit slop panel out there.

    You're absolutely right, my friend. That's why I built this control panel and tested it for a full year. It was CLI-only at first, but I've now developed a graphical interface for it. You can try it out and evaluate it, and I genuinely welcome your honest feedback, no matter what it is. Your opinion means a lot to me, my friend.

    You thought having all these AI slop panels is bad, so you started your own AI slop panel?
    You might should get a better AI to outsource your thinking.

  • @Alyx said:

    @amerghjjiye said:

    @Alyx said:
    If only I would get a dollar for each crappy bullshit slop panel out there.

    You're absolutely right, my friend. That's why I built this control panel and tested it for a full year. It was CLI-only at first, but I've now developed a graphical interface for it. You can try it out and evaluate it, and I genuinely welcome your honest feedback, no matter what it is. Your opinion means a lot to me, my friend.

    You thought having all these AI slop panels is bad, so you started your own AI slop panel?
    You might should get a better AI to outsource your thinking.

    AI only assisted me with the visual identity, security testing, proofreading, and documentation. The engineering decisions and implementation are my own, built on 15 years of experience in networking and server infrastructure...
    This is a personal project I chose to release for free, not a commercial product. I’d appreciate technical criticism based on actual flaws rather than assumptions about how AI was used.

  • AlyxAlyx Member, Host Rep

    The same response as always.. Trust me bro, I did this myself, AI just helped with UI.
    Don't criticize the slop, instead do free bug testing for me...

    I'm getting tired of this... Pretty sure we all get tired of this.

    But hey, since you panel is free, and you seem to know how to use GitHub, feel free to prove me wrong, make the panel open source, so we all can see your 1yr history of "developing" this.

  • @Alyx said:
    The same response as always.. Trust me bro, I did this myself, AI just helped with UI.
    Don't criticize the slop, instead do free bug testing for me...

    I'm getting tired of this... Pretty sure we all get tired of this.

    But hey, since you panel is free, and you seem to know how to use GitHub, feel free to prove me wrong, make the panel open source, so we all can see your 1yr history of "developing" this.

    You’re welcome to evaluate it through the CLI if that’s your preferred approach. I’m not trying to convince everyone to use my panel or claim it’s perfect.

    I’ve spent years developing and using it on my own servers, and I’m sharing it because I believe it could benefit the community. Even if I’m the only person who uses it, that’s still worthwhile to me.

    What I genuinely want to learn is whether it can meet real-world security standards and offer a reliable, practical experience for other administrators. I can judge my own work only to a certain extent; independent technical review is what helps uncover the weaknesses I might have missed.

  • AlyxAlyx Member, Host Rep

    If you want independent technical reviews, open source your project.
    So people can actually review it.

  • @Alyx said:
    If you want independent technical reviews, open source your project.
    So people can actually review it.

    Perhaps I’ll make the source code public once I’ve cleaned it up and prepared it for others to work with reliably. Some parts of the code have minor issues that can cause significant problems during development, mainly due to the many changes I’ve made to the CLI over time. Once you look at the code, you’ll understand what I mean. I want to address these issues first before opening it up to the community.

    func paanelcertProp(cfg *config.Config, domain string) *security.Text {
    certPath, err := cfg.DomainCert()
    if err != nil {
    return certError(
    "تعذر تحديد مسار شهادة نطاق اللوحة.",
    "Unable to determine the panel certificate path.",
    )
    }

    certPEM, err := os.ReadFile(certPath)
    if err != nil {
        return certError(
            "شهادة نطاق اللوحة مفقودة أو يتعذر قراءتها.",
            "The panel certificate is missing or unreadable.",
        )
    }
    
    block, _ := pem.Decode(certPEM)
    if block == nil || block.Type != "CERTIFICATE" {
        return certError(
            "ملف شهادة نطاق اللوحة غير صالح.",
            "The panel certificate file is invalid.",
        )
    }
    
    cert, err := x509.ParseCertificate(block.Bytes)
    if err != nil {
        return certError(
            "تعذر تحليل شهادة نطاق اللوحة.",
            "Unable to parse the panel certificate.",
        )
    }
    
    if err := cert.VerifyHostname(domain); err != nil {
        return certError(
            "الشهادة لا تطابق نطاق اللوحة "+domain+".",
            "The certificate does not match the panel domain "+domain+".",
        )
    }
    
    now := time.Now()
    
    if now.Before(cert.NotBefore) {
        return certError(
            "لم يبدأ سريان شهادة نطاق اللوحة بعد.",
            "The panel certificate is not valid yet.",
        )
    }
    
    remaining := time.Until(cert.NotAfter)
    
    if remaining <= 0 {
        return certError(
            "انتهت صلاحية شهادة نطاق اللوحة. اضغط «أصلح تلقائيًا» لتجديدها.",
            "The panel certificate has expired. Press “Fix automatically” to renew it.",
        )
    }
    
    if remaining < 10*24*time.Hour {
        days := int(remaining.Hours() / 24)
    
        return certError(
            fmt.Sprintf(
                "تنتهي صلاحية شهادة نطاق اللوحة خلال %d يومًا. تحقق من إعدادات النطاق ثم اضغط «أصلح تلقائيًا».",
                days,
            ),
            fmt.Sprintf(
                "The panel certificate expires in %d days. Check the domain configuration, then press “Fix automatically”.",
                days,
            ),
        )
    }
    
    return nil
    

    }

    func certError(ar, en string) *security.Text {
    msg := sys.T(ar, en)
    return &msg
    }

    func panelCertProbleError2(cfg *config.Config, domain string) *security.Text {
    // certPath, err := cfg.DomainCert()
    // if err != nil {
    // return certError(
    // "تعذر تحديد مسار شهادة نطاق اللوحة.",
    // "Unable to determine the panel certificate path.",
    // )
    // }

    // certPEM, err := os.ReadFile(certPath)
    // if err != nil {
    //     return certError(
    //         "شهادة نطاق اللوحة مفقودة أو يتعذر قراءتها.",
    //         "The panel certificate is missing or unreadable.",
    //     )
    // }
    
    // block, _ := pem.Decode(certPEM)
    // if block == nil || block.Type != "CERTIFICATE" {
    //     return certError(
    //         "ملف شهادة نطاق اللوحة غير صالح.",
    //         "The panel certificate file is invalid.",
    //     )
    // }
    
    // cert, err := x509.ParseCertificate(block.Bytes)
    // if err != nil {
    //     return certError(
    //         "تعذر تحليل شهادة نطاق اللوحة.",
    //         "Unable to parse the panel certificate.",
    //     )
    // }
    
    // if err := cert.VerifyHostname(domain); err != nil {
    //     return certError(
    //         "الشهادة لا تطابق نطاق اللوحة "+domain+".",
    //         "The certificate does not match the panel domain "+domain+".",
    //     )
    // }
    
    // now := time.Now()
    
    // if now.Before(cert.NotBefore) {
    //     return certError(
    //         "لم يبدأ سريان شهادة نطاق اللوحة بعد.",
    //         "The panel certificate is not valid yet.",
    //     )
    // }
    
    // remaining := time.Until(cert.NotAfter)
    
    // if remaining <= 0 {
    //     return certError(
    //         "انتهت صلاحية شهادة نطاق اللوحة. اضغط «أصلح تلقائيًا» لتجديدها.",
    //         "The panel certificate has expired. Press “Fix automatically” to renew it.",
    //     )
    // }
    
    // if remaining < 10*24*time.Hour {
    //     days := int(remaining.Hours() / 24)
    
    //     return certError(
    //         fmt.Sprintf(
    //             "تنتهي صلاحية شهادة نطاق اللوحة خلال %d يومًا. تحقق من إعدادات النطاق ثم اضغط «أصلح تلقائيًا».",
    //             days,
    //         ),
    //         fmt.Sprintf(
    //             "The panel certificate expires in %d days. Check the domain configuration, then press “Fix automatically”.",
    //             days,
    //         ),
    //     )
    // }
    path, _ := cfg.DomainCert()
    bad := func(ar, en string) *security.Text { t := sys.T(ar, en); return &t }
    b, err := os.ReadFile(path)
    if err != nil {
        return bad("اللوحة مربوطة بالنطاق "+domain+" لكن شهادته مفقودة. اضغط «أصلح تلقائيًا» لإصدارها من جديد.",
            "The panel is tied to "+domain+" but its certificate is missing. Press “Fix automatically” to issue it again.")
    }
    block, _ := pem.Decode(b)
    if block == nil {
        return bad("شهادة نطاق اللوحة تالفة.", "The certificate of the panel's domain is damaged.")
    }
    cert, err := x509.ParseCertificate(block.Bytes)
    if err != nil || cert.VerifyHostname(domain) != nil {
        return bad("الشهادة المحفوظة ليست للنطاق "+domain+".", "The certificate on file is not for "+domain+".")
    }
    if left := time.Until(cert.NotAfter); left < 10*24*time.Hour {
        return bad(fmt.Sprintf("شهادة نطاق اللوحة تنتهي بعد %d يوم ولم تتجدد. تأكد أن النطاق ما زال يشير إلى السيرفر، ثم اضغط «أصلح تلقائيًا».", max(int(left.Hours()/24), 0)),
            fmt.Sprintf("The certificate of the panel's domain runs out in %d days and has not renewed. Make sure the domain still points at the server, then press “Fix automatically”.", max(int(left.Hours()/24), 0)))
    }
    return nil
    

    }

  • mans_xdmans_xd Member

    انا شايف في عربي ف الموضوع المهم هسيبك مع الشباب هنا هما كفايه anti slop لوحدهم

    Thanked by 1amerghjjiye
  • اكيد التطبيق > @mans_xd said:

    انا شايف في عربي ف الموضوع المهم هسيبك مع الشباب هنا هما كفايه anti slop لوحدهم

    هو بقول حق بصراحة وانا جديد على هاد الموقع بصراحة وهو عشان ما يضيع وقت هو مفكر انو التطبيق كامل مصنوع بال ai

  • @mans_xd said:
    انا شايف في عربي ف الموضوع المهم هسيبك مع الشباب هنا هما كفايه anti slop لوحدهم

    فينك تتأكد وتجرب اللوحة وتعطيني رأيك فيها ك أمان وك عمليات واكون لك من الشاكرين

  • skyandseaskyandsea Member

    Perhaps I’ll make the source code public once I’ve cleaned it up and prepared it for others to work with reliably.

    Why does it need to be cleaned up? you can just ignore any PRs lol. Why don't these AI slop creators just own it? Human intelligence will cease to exist within a few years anyways. I'd respect you more if you just own it.

    Yeah I use AI so what?

  • @skyandsea said:

    Perhaps I’ll make the source code public once I’ve cleaned it up and prepared it for others to work with reliably.

    Why does it need to be cleaned up? you can just ignore any PRs lol. Why don't these AI slop creators just own it? Human intelligence will cease to exist within a few years anyways. I'd respect you more if you just own it.

    Yeah I use AI so what?

    You’re right, my friend. The real problem is the misuse of AI. When AI reorganizes files or modifies code and the developer doesn’t understand what changed or how it works, that’s where things become dangerous.

    I agree with you on that. I used AI to help with the visual identity, but it sometimes suggests solutions that actually get in my way, especially when it comes to security vulnerabilities. That’s why I believe AI should be a tool to assist developers, not a replacement for understanding the code and taking responsibility for it.

  • @skyandsea said:

    Perhaps I’ll make the source code public once I’ve cleaned it up and prepared it for others to work with reliably.

    Why does it need to be cleaned up? you can just ignore any PRs lol. Why don't these AI slop creators just own it? Human intelligence will cease to exist within a few years anyways. I'd respect you more if you just own it.

    Yeah I use AI so what?

    Even organizing technical documentation has become something AI does better than I do, so I take advantage of that too. There’s nothing wrong with using tools that make our work more efficient. These days, almost every developer consults AI to learn how to approach a problem or implement something. The real difference is whether you understand the results, can evaluate their quality, and take responsibility for what you build.

Sign In or Register to comment.