Howdy, Stranger!

It looks like you're new here. If you want to get involved, click one of these buttons!


Home β€Ί General
New on LowEndTalk? Please Register and read our Community Rules.

All new Registrations are manually reviewed and approved, so a short delay after registration may occur before your account becomes active.

ioflood got hacked !!!!!!

tauseeftauseef Member
edited September 26 in General

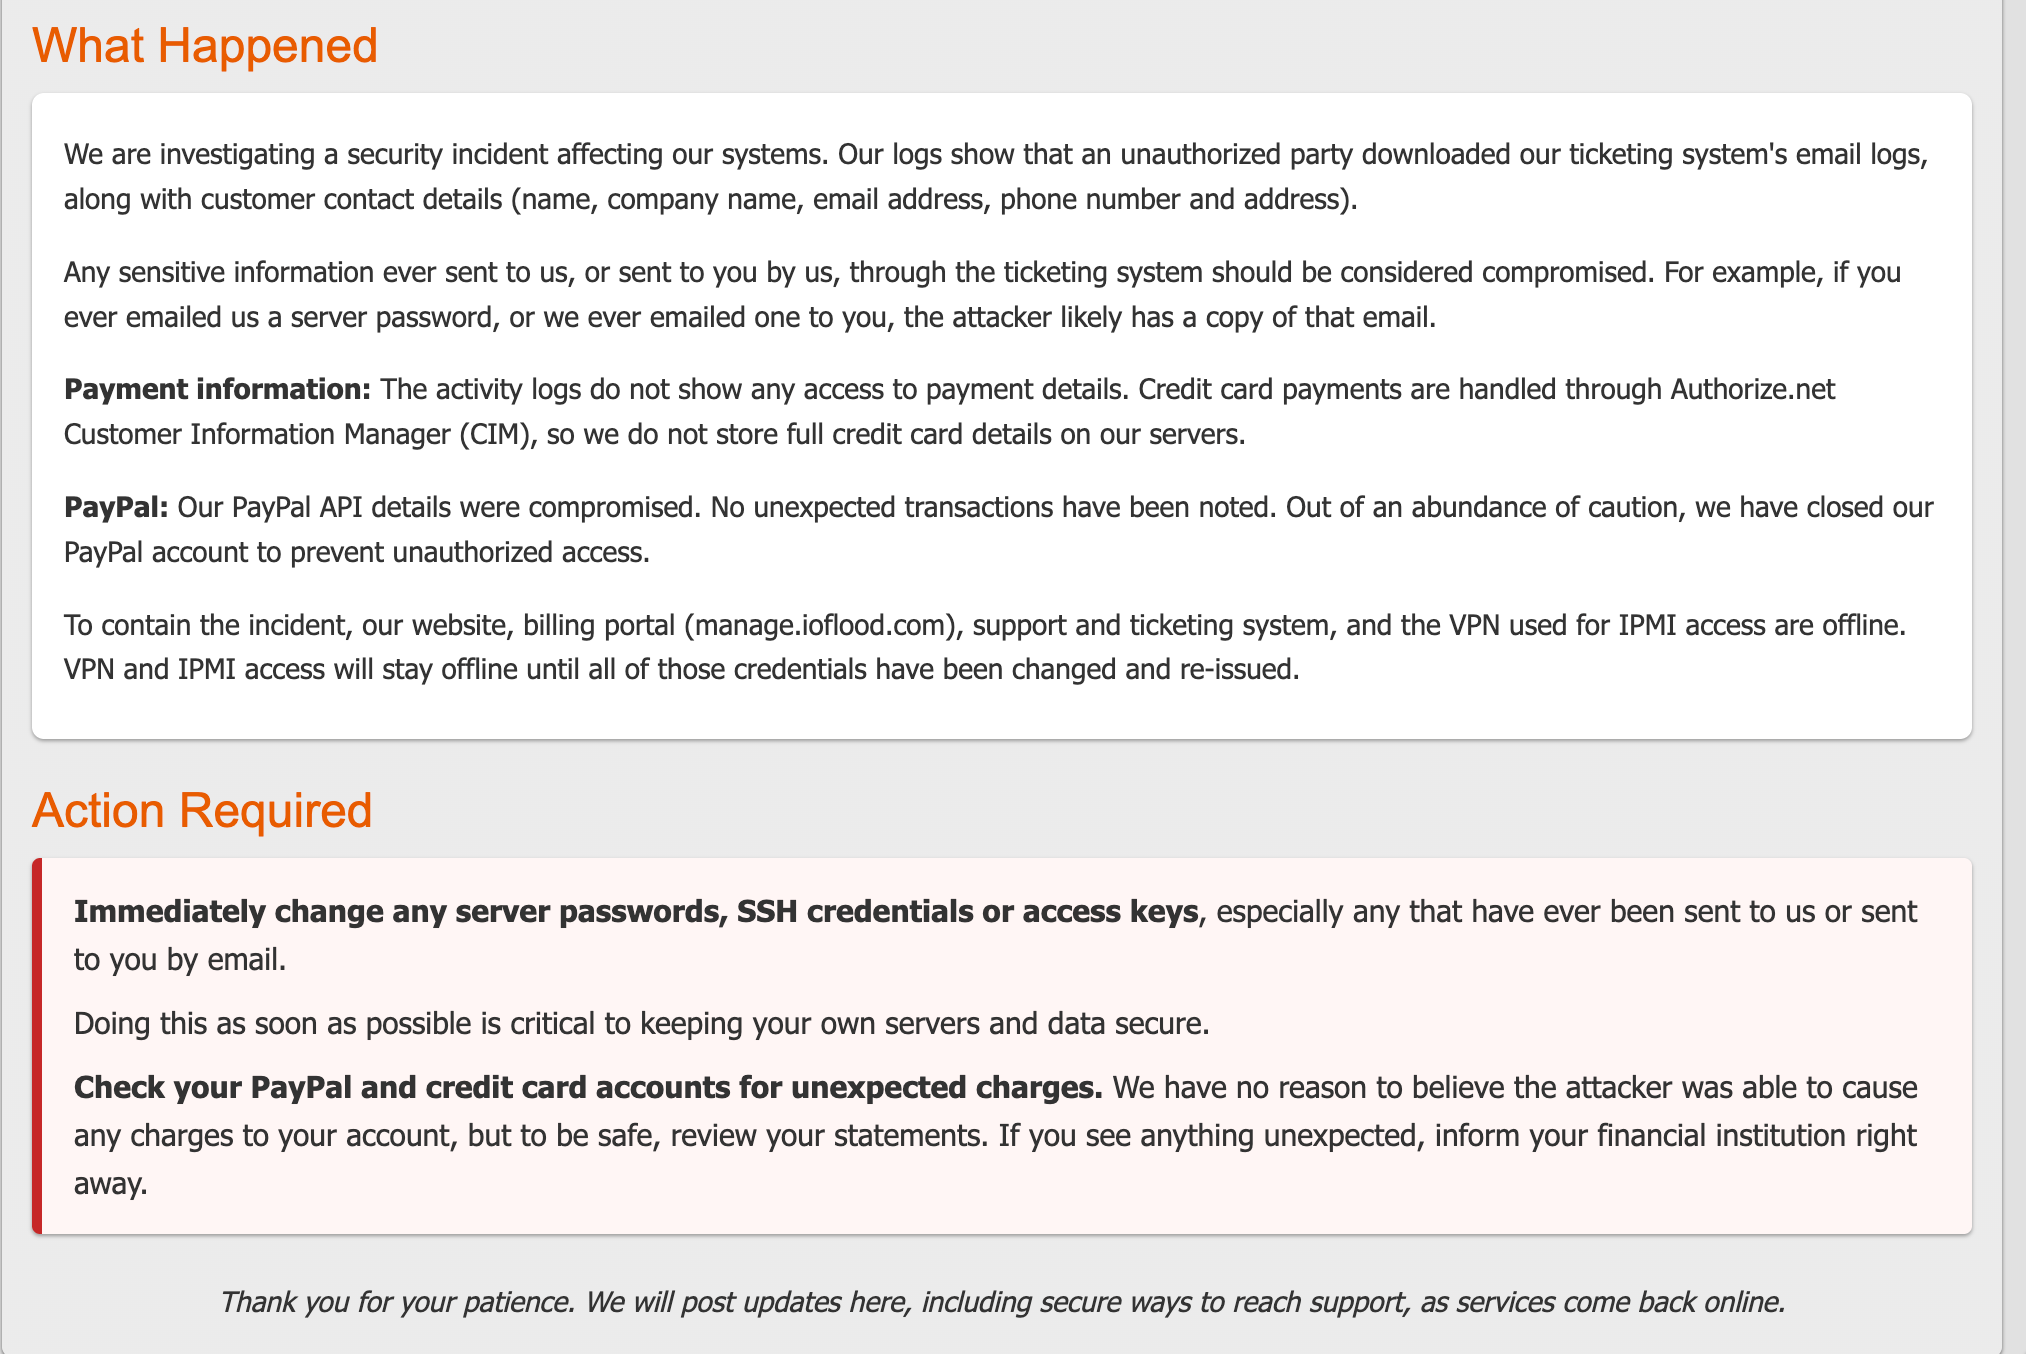
If anyone using https://ioflood.com/ , take safety precautions
Thanked by 1MikeDVB
Comments

  • oh no... well

    Thanked by 1COLBYLICIOUS
  • zedzed Veteran

    closed their paypal account to prevent unauthorized access, what?

  • Another day, another breach.

    Thanked by 1COLBYLICIOUS
  • angstromangstrom Moderator, Veteran

    In principle, there's a user @ioflood_michael_b here, but they were last active in May 2023, also zero posts, so I wouldn't hold my breath to hear from them

    Thanked by 1COLBYLICIOUS
  • oh no.

  • Never even heard about these guys.

  • @zed said:
    closed their paypal account to prevent unauthorized access, what?

    They closed their paypal account to prevent unauthorized access

  • Unlike others in similar situations ioflood don't say they have everything under control and there are no reasons to worry.

    Thanked by 1Plioser
  • NameBigNameBig Member, Patron Provider

    @JohnFilch123 said:

    @zed said:
    closed their paypal account to prevent unauthorized access, what?

    They closed their paypal account to prevent unauthorized access

    closed their paypal account to prevent unauthorized access, what?

    Thanked by 2zafouhar thane
  • @NameBig said:

    @JohnFilch123 said:

    @zed said:
    closed their paypal account to prevent unauthorized access, what?

    They closed their paypal account to prevent unauthorized access

    closed their paypal account to prevent unauthorized access, what?

    Yes.

  • @JohnFilch123 said:
    Never even heard about these guys.

    Their stomping grounds is WHT. Interestingly enough, the topic of their last VPS offer posted on 09-22-26 is "1TBVPS WHT Exclusive! KVM VPS with NO Compromises!"

    Compromises have occurred. The irony. Best wishes to all impacted.

  • @rogerwilco said:

    @JohnFilch123 said:
    Never even heard about these guys.

    Their stomping grounds is WHT. Interestingly enough, the topic of their last VPS offer posted on 09-22-26 is "1TBVPS WHT Exclusive! KVM VPS with NO Compromises!"

    Compromises have occurred. The irony. Best wishes to all impacted.

    ahhh shitt

  • zedzed Veteran

    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    Thanked by 1buggedout
  • @zed said:
    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    I remembered this after reading your comment....

    @totally_not_banned said:
    You should rename yourself to pechgoblin. Whenever you post something terrible has happened.

    Thanked by 1rpqu
  • @zed said:
    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    :/ banned for ?

  • @tauseef said:

    @zed said:
    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    :/ banned for ?

    For existing /s
    πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚

  • @rpqu said:

    @tauseef said:

    @zed said:
    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    :/ banned for ?

    For existing /s
    πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚

  • @tauseef said:

    @rpqu said:

    @tauseef said:

    @zed said:
    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    :/ banned for ?

    For existing /s
    πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚

    Yeah, it's just a joke

  • Do you stash clouds?

  • jbilohjbiloh Administrator, Veteran

    Looks bad.

    Has there been any recent customer communication?

  • OhJohnOhJohn Member
    edited September 27

    @jbiloh They sent out a mail. Even to former customers.

  • @angstrom said: In principle, there's a user @ioflood_michael_b here, but they were last active in May 2023, also zero posts, so I wouldn't hold my breath to hear from them

    I'd rather ask @funkywizard but has been last active in Aug 2023....

  • OhJohnOhJohn Member
    edited September 27

    The question is: is this just IOFLOOD or is there a prob in the panel they use (will not name the panel now as there are some other providers using the same...)

  • MikeAMikeA Patron Provider, Veteran
    edited September 27

    @JohnFilch123 said:
    Never even heard about these guys.

    IOFlood is a very old company. I used them back in like 2012 or something when I was younger and didn't have any experience with servers (was running a Minecraft community.) Good company if Gabriel/funkywizard still runs it, he was always willing to help me back then and I'm forever grateful. It's not a low end server provider so I'd be surprised if anyone here used them except other companies for something niche.
    Edit - He posted an update on WHT yesterday https://www.webhostingtalk.com/showthread.php?t=1963746&p=10516965#post10516965

  • @JohnFilch123 said:
    Never even heard about these guys.

    they are very active in webhostingtalk, has sticky ad post in the dedicated server offers section for a long time

  • oh noo !!

  • ahhh

  • @OhJohn said:
    The question is: is this just IOFLOOD or is there a prob in the panel they use (will not name the panel now as there are some other providers using the same...)

    It's not an issue with Ubersmith specifically. They clarified in an e-mail the breach was due to their Ubersmith API key being exposed as their website was compromised. Their website was in-house developed so there's no risk to other providers.

    @MikeA said:

    @JohnFilch123 said:
    Never even heard about these guys.

    IOFlood is a very old company. I used them back in like 2012 or something when I was younger and didn't have any experience with servers (was running a Minecraft community.) Good company if Gabriel/funkywizard still runs it, he was always willing to help me back then and I'm forever grateful. It's not a low end server provider so I'd be surprised if anyone here used them except other companies for something niche.
    Edit - He posted an update on WHT yesterday https://www.webhostingtalk.com/showthread.php?t=1963746&p=10516965#post10516965

    Yeah Gabriel still runs it, and in my experience they're a very good provider. Outages are extremely rare and whenever I've talked to support, they've been good. They're not a Low End provider at all, but they do sometimes post decent deals and I managed to pick up a storage box for a very affordable price a couple years ago which has gone from a good deal to a bargain as prices have crept up so much.

    @jbiloh said:
    Looks bad.

    Has there been any recent customer communication?

    Yeah, they've been sending out an absolute flood of e-mails for this.

    Initial e-mail sent Wed, 23 Sep 2026 23:59:58 +0000

    Dear Valued Customer,

    We are writing to inform you that we are currently investigating a security incident affecting our systems.

    Out of an abundance of caution, we STRONGLY URGE all customers to IMMEDIATELY change any server passwords, SSH credentials, or access keysβ€”especially any that have ever been shared with us or sent to you via email.

    Our logs show that an unauthorized party downloaded our ticketing system's email logs, as well as customer contact details (customer name, company name, email address, phone number, address).

    We are continuing to investigate the full scope of the security breach. In the meantime, our support, billing, vpn, and website systems remain offline in order to prevent further unauthorized access.

    As a result, any sensitive data ever sent to us or sent to you via the ticketing system should be considered compromised.

    For example:

    If you have ever sent us your server password, the attacker likely has a copy of that email.

    If we have ever sent you a password via email, the attacker likely has a copy of that email.

    Payment Information Status: The activity logs do not show that the attacker gained access to any payment details. Additionally, we use Authorize.net Customer Information Manager (CIM) for credit card payments. This means that we do not store full credit card details for customers on our servers.

    Action Required

    We STRONGLY URGE all customers to IMMEDIATELY change any server passwords, SSH credentials, or access keysβ€”especially any that have ever been sent to us via email or sent to you via email.

    Taking this action as soon as possible is critical to ensuring your servers and data remain secure from a potential breach of your own.

    Measures Taken & Current System Operations

    To isolate the impacted systems and prevent further risk, we have taken several proactive measures:

    Company Website & Billing System: ioflood.com and manage.ioflood.com are currently offline. We will bring them back online as soon as it is safe to do so.

    VPN & IPMI Access: Because VPN and IPMI login details can be sent to customers via email, we have temporarily disabled the VPN server used for IPMI access. This service will remain offline until all IPMI and VPN credentials can be changed and re-issued.

    Support System: The support and ticketing system is currently offline while we secure it.

    Next Steps & Communication

    The support and ticketing system is currently offline while we secure it but we are still

    To re-iterate: we strongly urge all customers to change any passwords and credentials that may have been sent to us or sent by us at any time.

    Thank you for your patience and cooperation as we work through this security incident.

    Sincerely,
    The IOFLOOD Team

    Followup e-mail 7 minutes later (Thu, 24 Sep 2026 00:07:12 +0000)

    Dear Valued Customers

    I wanted to provide an addendum to the previous email regarding the security incident.

    For currently existing customers, if you need support please email us directly at [email protected] as we are able to communicate via that channel at this time. You will not be able to access the support portal, but direct email is usable at that time.

    Thank you

    Followup e-mail about PayPal, which I don't use so I think they just blasted to everyone regardless (Fri, 25 Sep 2026 18:35:57 +0000)

    Dear IOFLOOD Customer,

    DO NOT send any PayPal payments to [email protected] moving forward. We will not receive them.

    As part of our investigation into the recent security breach affecting IOFLOOD systems, we determined that the attacker gained access to API credentials used by IOFLOOD to communicate with PayPal.

    Those API credentials were disabled as soon as we became aware of the breach.

    We reviewed the available PayPal API logs and transaction history and did not identify any unexpected API activity or unauthorized transactions associated with our account.

    However, PayPal support was unable to provide us with sufficient information regarding the full extent of access the exposed API credentials may have provided. They were also unable to confirm whether the API activity visible to us in our PayPal account represented a complete record of all API activity associated with those credentials. As a result, we could not rely on the visible logs alone to conclusively determine that no unauthorized API activity had occurred. Additionally, PayPal support was unable to provide us with enough assurance that all necessary steps had been taken to fully secure the account following the exposure of those credentials.

    Because we were not comfortable leaving any uncertainty around the security of the account, we have closed the PayPal account associated with [email protected].

    DO NOT send any PayPal payments to [email protected] moving forward. We will not receive them.

    In addition, all existing PayPal subscriptions and billing agreements associated with this account are no longer valid and should not be relied upon for future renewals.

    Although we have not identified any unauthorized PayPal activity, we strongly encourage customers to review their recent PayPal and credit card activity and report any transactions they do not recognize to their payment provider or financial institution.

    At this time, we do not have a firm timeline for establishing a new PayPal account. Customers should plan to use a credit card for their next renewal once our billing system is restored.

    Please note that IOFLOOD is not currently accepting payments through any payment method while our billing system remains offline. We will notify customers when billing services have been restored and payments can resume.

    If you have any questions about this change, you can reply directly to this email or contact us at [email protected].

    Thank you for your patience and cooperation while we continue working through this incident.

    Sincerely,

    The IOFLOOD Team

    Next status update Fri, 25 Sep 2026 19:12:15 +0000

    Dear IOFLOOD Customer,

    We are continuing our investigation into the recent security incident affecting IOFLOOD systems and wanted to provide an update on our progress.

    As described in our initial notification, we found that an unauthorized party accessed and downloaded our support portal email logs and customer contact information. Our investigation has since identified that credentials used by IOFLOOD to access PayPal's API were also exposed.

    Our impacted PayPal credentials were disabled as soon as we became aware of the breach. We reviewed the available PayPal API logs and transaction history and have not identified any unexpected activity or unauthorized transactions. However, PayPal support was unable to provide us with sufficient information about the extent of access the exposed API credentials may have provided, or enough assurance that all necessary steps had been taken to fully secure the account. Because of that uncertainty, we closed our PayPal account to ensure that no further unauthorized activity can occur through it.

    You can find additional information about the PayPal account closure and what it means for customers in the email we sent earlier today.

    Additionally, even though we did not identify any unauthorized payment activity, we strongly encourage customers to review their recent PayPal and credit card activity for any charges they do not recognize.

    Other Systems

    Our investigation into the rest of our systems is still ongoing. We are continuing a detailed root cause and scope analysis so that we can be certain we fully understand how the breach occurred, what systems and data were affected, and that the incident has been completely contained.

    Once we are confident that we have established the full scope of the incident and confirmed containment, we will identify and complete any remaining steps necessary to fully secure the affected systems before bringing them back online. Until that time, our billing system, support system, ordering system, and VPN will remain offline until we are satisfied that they can be safely restored.

    So far, our investigation has not identified evidence that customer records were modified, but we want to be absolutely certain of this before restoring the billing and support system. With that in mind, once we have firmly established the initial date of the breach, we will compare the current database against backup data from before that date. This will allow us to carefully identify any unexpected changes.

    We understand the importance of restoring these services as quickly as possible, but we do not want to bring them back online until we are confident in both their security and the integrity of the underlying data.

    Phishing Precautions

    Because customer contact information was exposed during this incident, we also want to remind customers to be especially cautious about phishing attempts or other communications pretending to originate from IOFLOOD.

    Please keep the following precautions in mind:

    Be cautious of unexpected emails, phone calls, or messages claiming to be from IOFLOOD, particularly messages attempting to create a sense of urgency.
    Carefully verify the sender's email address rather than relying only on the displayed sender name.
    Avoid clicking links in unexpected messages. When possible, navigate directly to IOFLOOD services using an address you already know rather than following a link contained in an email.
    Do not provide passwords, authentication codes, SSH keys, or other account credentials in response to an unsolicited message.
    Be particularly suspicious of unexpected requests involving payments, password resets, account changes, server access, or changes to contact information.
    If you are unsure whether a communication claiming to be from IOFLOOD is legitimate, please verify it with us before taking any action.
    

    Important: Change Previously Shared Credentials

    We also want to reiterate the most important recommendation from our initial notice: if any server passwords, SSH credentials, access keys, or other sensitive credentials have ever been sent to us or sent to you through our ticketing system or email, they should be considered compromised and should be changed if you have not already done so.

    Although the normal support system remains offline, you can still reach us with any questions, concerns, or requests for assistance by replying directly to this email or by emailing [email protected]. Our team is continuing to monitor and respond to incoming messages.

    We will provide additional updates as our investigation progresses and as further information is confirmed.

    Thank you for your patience and cooperation while we work through this incident.

    Sincerely,

    The IOFLOOD Team

    September 26 status update sent at Sat, 26 Sep 2026 23:43:06 +0000 which includes some root cause information

    Dear IOFLOOD customers,

    Thank you to everyone who has reached out providing moral support and encouragement in this difficult time. I want to assure you that our team has been working diligently to address this incident in the most careful and responsible way possible to minimize potential negative impacts to you, our customers.

    I wanted to provide you an update on our incident response.

    We believe we have determined the root cause of the breach of our ioflood.com website webserver. We believe a breach of that server was the entry point for the attacker, and we believe we understand the scope of that breach and what the attackers would have had access to as a result. We are still investigating that server to ensure that we didn't overlook anything.

    We have also determined the first date of unauthorized access to our billing system manage.ioflood.com. We have also determined that the unauthorized access to that server occured solely via an api key that was obtained from the breach of the ioflood.com website webserver.

    We are in the final stages of evaluating the manage.ioflood.com (Ubersmith) billing / support database and related logs.

    Luckily, the Ubersmith billing portal includes very detailed logs of all activity, giving us confidence in those results. We also maintain frequent backups of this data that we are actively comparing against.

    Our results of investigating the mysql binlog, web server logs, and api logs, leads us to believe that the attacker did not change existing user data and did not perform destructive actions.

    To be certain of this, we are currently running a diff between several different copies of the database taken at different times. If that comparison also comes up clean, we will be confident we can use the most up to date copy of the billing and support database.

    At the current pace of work, we expect to have these results sometime tomorrow. If those results come back clean, we plan to enable access to the manage.ioflood.com billing / support panel shortly thereafter.

    Because the compromise involved unauthorized use of our Ubersmith API key, we are planning to do a thorough audit of all the ways our custom software uses the Ubersmith API, and adjust code and security practices to minimize the possibility of future abuse. In the meantime, we have blocked the ability of the Ubersmith API to be accessed whatsoever.

    Because such an audit will take quite some time, our plan is to disable all IOFLOOD-customized features of the billing portal that require the API to function.

    Once we have configured the manage.ioflood.com billing / support portal to operate without API functionality, and we have concluded our investigation of the database integrity, we will bring the manage.ioflood.com portal back online for customer access. This could happen as early as tomorrow.

    Authorize.net based credit card billing was not impacted by this breach. The attacker was not able to access sensitive data related to this system. Customer card data and profiles are stored on Authorize.net systems in tokenized form so that IOFLOOD systems have no access to that data after it is handed off to Authorize.net.

    Because of that, we plan to bring credit card billing back online one day after the portal is made available to customers. Customers whose services are set to charge automatically who have a credit card on file, will be charged by our system automatically on the regular nightly run that day. At that time, customers will also be able to add new credit cards to pay for existing invoices.

    We are working to sign up for a new paypal account so that we can accept payments via paypal soon. We do not have an ETA on completing this. As a result, it would be greatly appreciated if customers could arrange to pay their next renewal via credit card instead of paypal. If this is not possible for you, or you have any concerns with this, please let us know and we will do our best to help.

    We will reach back out again once the billing portal is back online or if there is any other important information to share.

    Thank you again for working with us as we as we work to resolve this unfortunate incident. I am deeply grateful for your patience and understanding.

    Sincerely,

    Gabriel Ramuglia
    President -- Input Output Flood, LLC
    We Love Servers

    Web: www.ioflood.com
    Email: [email protected]

    Update from today sent at Sun, 27 Sep 2026 16:59:11 +0000 (~15 minutes ago as I'm typing this)

    Dear IOFLOOD customers,

    I wanted to provide another update regarding our ongoing response to the recent security incident.

    We have completed the database comparisons discussed in our previous update, and those comparisons came back clean. Combined with our review of the MySQL binary logs, web server logs, API logs, and other available records, we are confident that the integrity of the most recent copy of our billing and support database has been maintained.

    As a result, access to the manage.ioflood.com billing and support portal has now been restored.

    At this time, however, we are not yet accepting PayPal or credit card payments through the portal.

    We are planning to re-enable credit card payments tomorrow.

    We are also continuing to work on getting our new PayPal account online so that we can resume accepting PayPal payments. In the meantime, we would greatly appreciate it if customers with upcoming renewals could arrange to make those payments by credit card instead of PayPal where possible. If paying by credit card is not possible for you, please let us know and we will do our best to work with you.

    As a reminder, some customers may have received an automated overdue invoice reminder during this period. We apologize for these messages, but please be assured that your servers are not currently at risk of suspension due to an unpaid invoice while we are not accepting payments. Once payment processing has been restored, we will provide customers an appropriate opportunity to bring any outstanding invoices current.

    You may also notice that some functionality previously available within the billing portal is currently missing. As part of our response to this incident, we have disabled access to the Ubersmith API while we perform a thorough security audit of our custom software and the ways in which it previously interacted with that API.

    Any IOFLOOD-customized code that relies upon the Ubersmith API is therefore not currently deployed. This includes the ability to manage server power from within the billing portal, along with some other customized functionality.

    These features will remain disabled while we complete our security review and make any changes we determine are necessary before allowing this functionality to return.

    We will continue to provide updates as payment processing and other functionality are restored, or if we identify any other important information that needs to be shared.

    Thank you again for your patience, understanding, and support while we work through this incident.

    Sincerely,

    IOFLOOD

    Thanked by 3zed itzsenu OhJohn
  • MannDudeMannDude Patron Provider, Veteran

    Now that's a name I've not heard in a while.

    I just remember them being active on WHT 10-15 years ago offering, I believe... VM's in Arizona and you could have dedicated HDDs attached to them?

  • @rpqu said:

    @tauseef said:

    @zed said:
    this @tauseef guy has been nothing but bad news and being weird since he showed up, should probably be banned.

    :/ banned for ?

    For existing /s
    πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚πŸ˜‚

    Oh much more than just that, https://lowendtalk.com/discussion/221549/usa-phoenix-noble-vps-kvm-herald-7-70-mo-code-let-windows-linux-nvme 🍿

Sign In or Register to comment.